Tag: CCNP

  • Network Fundamentals: The OSI Model

    Network Fundamentals: The OSI Model

    Networking is one of the fundamental pillars of computing.  Networks allow us to communicate data across a global scale in a way which largely seems (to me) to be taken for granted.  Networking, even on the most basic of levels, is a skill that will aid anyone in technology will find valuable to their career – from system administrators, to help desk, to programmers.

    I will be starting off with a simple description of what networking is, then going through some basic terminology, introducing the OSI model, describing local versus routable network traffic, some basic network troubleshooting tools, and finally ending with a high-level overview of some of the most basic network protocols such as HTTP and DNS.

    My hope is that – even if I don’t inspire the same level of interest in you that I have with networking – you do come away learning something.

    What is Networking? 

    Networks allow two devices to talk to each other and transmit application data, whether they’re as close together as being in the same room or as far as being half a world apart.  Accomplishing this involves a basic, standardized process for how two devices – with no prior knowledge of the other’s location – can send information back and forth.

    At its highest level, the Internet is a network.  This is the one network that I’m sure everyone reading this post is aware of.  On a more granular level, though, a network can be as small as a Bluetooth device connecting to your phone (known as a Personal Area Network, or PAN).  If you have a modem or router at home that allows multiple devices to connect through your Internet Service Provider, you have a Local Area Network (LAN).

    In order to accomplish this, we use network devices.  The most common of these are the switch and the router.  Earlier devices like hubs and bridges did once exist, but have mostly gone the way of the dinosaur.  The primary differences between these devices is found in how they handle network communications, also known as traffic.

    Switches aggregate incoming traffic from each physical port (also known as an interface) and forward it on to its destination.  If the intended recipient is directly connected to the same switch as the sending device, then the switch will forward that traffic directly from the sender to the destination device.  If the recipient is not directly connected to the same switch as the sending device then one of two things happens:

    • The switch has learned where the recipient is connected on a neighboring network device (switch or router) and forwards that traffic to the neighboring network device; or
    • The switch has never seen the intended recipient before, does not know where it is located on the network, and sends the traffic out of every interface except the interface that traffic was received on.  This is known as a flood.

    Routers, on the other hand, are meant to take network traffic from switches destined to a different network than the originating network.  As an example, if you were to open a web browser and open google.com, your network router would take that traffic and forward it out to the internet for Google’s network to respond to.  I will get more into this a little further down when I go over local versus routable network addressing.

    Some routers – either home routers which are manufactured this way or business-class routers which are specifically configured this way – can service the same network from multiple interfaces.  For the sake of simplifying things in this post I will refer to routers specifically when traffic needs to be forwarded between two separate networks.

    The OSI Model

    When dealing with an abstract principle such as networking, it is helpful to have a logical representation to visualize concepts.  This is where the OSI model comes in.

    Back in the late 70s, work began on multiple fronts to establish a standard model for networks which resulted in several publications.  Possibly the most well-known of these is the Open Systems Interconnection – Basic Reference Model, colloquially known as the OSI model.  This was, according to Wikipedia anyway, first defined in 1978 by Hubert Zimmerman before being published in 1984 by the International Standards Organization as standard ISO 7498.  It is regularly referenced in day-to-day network administration and is one of the most important basic principles to learn in networking as a whole.

    I would be remiss at this point if I did not also mention the Internet Protocol Suite, also known as TCP/IP, but sometimes also referred to as the TCP/IP model.  The Internet Protocol Suite is not really a model so much as it is an architecture which specifies how data is packetized, addressed, transmitted, routed, and received over a network.  Comparing the TCP/IP architecture with the OSI model is a bit of a nonstarter simply because they are two sides of the same coin.  Each compliments and builds upon the other.  Both share some of the same principles.  The most important difference is that the OSI model provides a more comprehensive breakdown of networking concepts while TCP/IP focuses on the nuts and bolts of implementing various protocols.

    The OSI model consists of seven layers arranged vertically in a stack, beginning on the bottom with Layer 1 and ending at the top with Layer 7.  These layers logically organize networking principles into separate groups in a way that is relatively easy to comprehend.  By understanding each of these layers, we can begin understanding both how TCP/IP architecture functions, as well as methodologies for troubleshooting connectivity when issues arise.
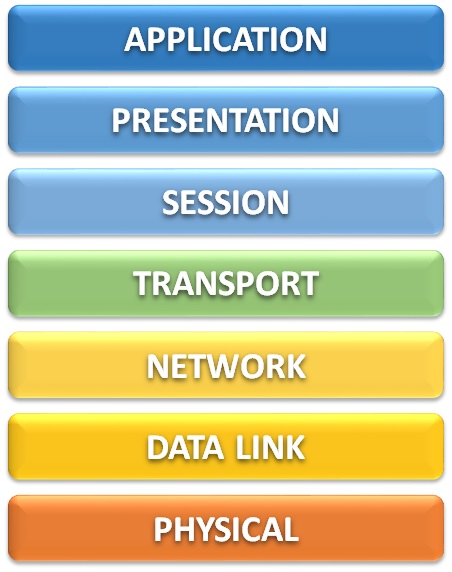
    This model can be broken down into two primary groupings – the Lower Layer (consisting of layers 1 through 4) and the Upper Layer (consisting of layers 5 through 7).

    The lower layers of the OSI model are the bread and butter of network administration.  These layers directly address how data flows across, into, and out of a network to other devices on that network or even out to the internet.

    On the other hand, the upper layers of the OSI model detail how that data is sent to and from the user’s application, as well as how that data is presented to the user – i.e., breaking down an email into multiple individual data packets, reassembling all of those packets in the correct order on the other side without losing any information, and presenting that email on the recipient’s inbox.

    Layer 7 – Application

    You could probably guess what this layer is, and you’d probably be right. The application layer consists of the programs that we as users interact with directly, such as web browsers or email clients. This also includes non-graphical network protocols which may be used from the command line or called in some other way (i.e., by the computer’s operating system) such as DHCP, FTP, and SNMP.

    Layer 6 – Presentation

    Presentation is a bang-on description of what the presentation layer does. This layer is responsible for the translation, compression, and encryption of application data before it is fed down to the lower-level layers, and again performs the reverse of these functions when fed receiving data by the session layer. The key benefit of this is that the presentation layer is in charge of ensuring that the recipient can understand what the sender is transmitting.

    Because not all data needs to go through a modification process to make data readable to a recipient, the presentation layer is sometimes skipped or otherwise performed by the application layer instead.

    Layer 5 – Session

    As data moves across the network, a conversation needs to be started between the sender and the receiver. This conversation is established, maintained, and eventually torn down by the session layer through the use of Application Program Interfaces (APIs). These APIs include NetBIOS, TCP/IP sockets, and Remote Procedure Calls (RPCs).

    The API conversations managed by the session layer differ from the TCP connections managed by the transport layer below in that the session layer manages these conversations on behalf of the application (the upper layers of the OSI model), whereas the transport layer manages its conversation on behalf of the network (the lower layers of the OSI model).

    Layer 4 – Transport

    Although I have already described the transport layer as one of the lower-level layers above, some of its functions could be said to be better described as upper-layer functions. If you look at all of the transport layer’s functionalities, though, it definitely skews more toward the lower (network) layers of the OSI model than the upper application layers.

    The transport layer primarily deals with the segmentation, packaging, and reassembly of data across the network through the connection-oriented Transmission Control Protocol (TCP) and connectionless User Datagram Protocol (UDP). It also insures the reliable delivery of quality network data by verifying that transmissions are received without errors and handling mismatches in speed to avoid overwhelming the receiver.

    Layer 3 – Network

    When I get asked what I do at work I usually try to summarize it somewhere along the lines of “I make sure that the computers can talk to each other.” The network layer is where the nuts and bolts of this communication really begin because this is where IP addresses come into play.

    Without an IP address — regardless of whether that is an IP version 4 address or an IP version 6 address — your computer isn’t going to get very far when attempting communication. When you attempt to browse to http://www.google.com, for instance, what really happens is that some DNS server translates the domain name (google.com) to an IP address (8.8.8.8).

    IP version 4 (IPv4) addresses consist of four sets of numbers between 0 and 255, called octets, which are separated by decimal points. There are public IP addresses which can be reached by anyone on the internet and private IP addresses which are reachable only from your local network. Of the private IP addresses, these are divided up into several groups known as classes — class A, class B, and class C being the most important. These directly relate to the maximum potential size for a network through something known as subnetting.

    IP version 6 (IPv6) addresses are much longer than IPv4 addresses and are made of up of hexadecimal characters — that is, numbers from 0 to 9 and letters from A to F. These addresses are 32 characters long and are broken up into eight groups called words which are separated by colons (:). They look something like this:

         2001:0db8:3333:4444:5555:6666:7777:8888

    Another very important function of the network layer is routing. Whatever your IP address is on your device, you will also have something called a gateway. If your computer is trying to communicate with another device outside of its subnet, then it will send that data to your gateway’s IP address. Your gateway will then route that traffic along the network based on its configuration.

    I may be a bit biased on this, but I feel like the data link layer is the most important of the lower layers.  This is where all the good stuff happens.  If the lower layers of the OSI model were a high school group project, layer 3 would be the jock that gets all the attention while layer 2 is the awkward kid that does all the actual work.
    Every device which connects to a network uses what is known as a Network Interface Controller, or NIC.  These NICs are technically a layer 1 component but they also contain what is arguably the most important component of the data link layer – a Media Access Control (MAC) Address.

    Each NIC has a MAC address which is assigned by the manufacturer.  (Sometimes these addresses are referred to as a burned-in address rather than a MAC address; it’s the same thing.)  These MAC addresses consist of 16 bits which are rendered in hexadecimal – that is, the only valid characters are 0 through 9, and A through F.

    MAC addresses can be presented in multiple logical formats which are usually divided into either six groups of two characters or three groups of four characters, often separated by a dot, colon, or hyphen.  The exact formatting of these MAC addresses doesn’t really matter too much.  They are written that way for much the same reason that phone numbers are written the way they are: for human benefit.  There are some exceptions to this in that the operating systems of network devices often require MAC addresses to be entered in a specific, consistent format.

    Layer 1 – Physical

    This layer consists of the physical wires and hardware necessary for computer networking.  That includes ethernet cables and network devices such as switches, routers, and firewalls.  Anything you can literally put your hands on, or any component piece of those such as internal electronics, is usually considered layer 1.

    Also included in layer 1 are the electrical impulses which are transmitted across the conductor wire, whether that is copper, fiber, or something else entirely.  (There is, I am given to understand, an actual RFC out there which defines the transmission of data across wet string, not to mention the well-known RFC for transmission by carrier pigeon.)

    Considerations

    In general, network traffic flows downward from Layer 7 to Layer 1 on the sending device, then upwards from Layer 1 to Layer 7 on the receiving device.  This is due to the way that operating systems break down application data into packets, frames, and ultimately the zeroes and ones which get transmitted across the wire.  Then, on the other side, the receiving device has to be able to know how to interpret those zeroes and ones, then reassemble them up the stack into application data.

    One thing to keep in mind is that the OSI model is not perfect.  It is a conceptual model.  You could visualize the OSI model as a 7-layer dip and not be entirely wrong.  Just like that same game day chip dip, you may not always hit every single layer in a single bite.  That’s okay.  Again…it’s a concept, not a ruleset.

  • Cisco ISE: Adding Network Devices

    In ISE, switches are referred to as a Network Access Device (NAD).  Other NAD devices include wireless LAN controllers and VPN concentrators.  NADs are responsible for enforcing ISE policies on devices connecting to the network with MAB authentication via RADIUS, as well as authorization of remote device administration over SSH via TACACS+.

    Before a switch will act as a NAD, it needs to be added to ISE as an object and configured for use as both a RADIUS and TACACS server with a shared key.

    To add a new switch to act as a NAD in ISE:

    1. Navigate to Administration > Network Resources > Network Devices.
    2. Click the + Add button.
    3. Configure the following attribute fields:
      1. Name: Type in the hostname of the switch.
      1. IP Address:         Type the management IP address of the switch.
      1. Location:            Click the drop-down and select Location.
      1. IPSEC:                 Click the drop-down and select Is IPSEC Device.
      1. Device Type:      Click the drop-down and select Device-Type.
    4. Click the checkbox next to RADIUS Authentication Settings and configure the Shared Secret.
    5. Click the checkbox next to TACACS Authentication Settings and configure the Shared Secret.
    6. Click the Submit button to complete the configuration.

    To edit the configuration of an existing device:

    1. Navigate to Administration > Network Resources > Network Devices.
    2. Click the checkbox next to the device to configure.
      Tip:  You can click the Show: drop down box and select Quick Filter option to search for a specific device using the Name or IP column.
    3. Click the Edit button.
  • Exam Review: Cisco SCOR 350-701

    I have been putting off writing this review for a year and a half now.  I did finally pass the SCOR exam and earn my CCNP Security certification, but only after four attempts and more hours than I care to try and estimate.  Don’t get me wrong – this is the first time I’ve ever framed a certification and hung it in my cubicle because I remember vividly what I went through to attain it.  I’m very happy and proud to have passed, but it seriously burned me out on studying for exams.

    After I passed the SISE exam in July of 2020, I immediately began studying for the SCOR exam.  My first attempt at it was in late September.  The next three attempts were all in the month of October, with my final passing result coming on October 24th.

    A major problem I had was specifically due to the official Cisco course guide being very scattered and irrelevant to the exam material, as well as my own lack of hands-on experience with any of the technologies covered by the exam apart from Identity Services Engine.  I also had some experience in studying for the retired IINS exam which included ASAs and VPNs, but I still do not have any experience with ESAs, WSAs, Umbrella, FirePOWER, or any of the other solutions covered by the SCOR.

    The greatest asset I had during my SCOR studies was a study group that was arranged by Martin B.(@martinmbne / mbne.net) for several of us who were all pursuing the CCNP Security certification.  We all shared our study notes, white papers we’d found, our wins, our losses, and they were a constant source of inspiration and motivation for me.  I would be remiss if I didn’t also mention Carl Zellers (@cfzellers4) and Kim Pedersen (@kpjungle / packet-forwarding.net) for offering their support and commiserations as I worked through my many exam attempts.

    Score Results

    This exam frustrated me for many reasons. One of those reasons is how close I came to passing on my second and third attempts. I’ve included the exam results of all of my attempts below for transparency.

    Exam TopicAttempt #1Attempt #2Attempt #3Attempt #4
    Security Concepts 80% 76% 84% 88%
    Network Security 52% 67% 67% 81%
    Securing the Cloud 67% 73% 80% 100%
    Content Security 64% 64% 71% 79%
    Endpoint Protection & Detection 70% 70% 50% 70%
    Secure Network Access, Visibility & Enforcement 80% 87% 80% 87%

    Study Materials and Cost

    For preparation, I used the following resources:

    CCNP and CCIE Security Core SCOR 350-701 Official Cert Guide (Cisco Press) – Cost: $73.60
    The nicest thing that I have to say about this book is that it I highly recommend it, at least as a starting point. You need to understand up front that this book does not do an adequate job of covering the exam material in enough detail — and honestly, doesn’t cover some exam material at all. You will not pass the SCOR exam solely by reading this book. If anything, my personal opinion is that this book gets you less than half the way there.

    Implementing and Operating Cisco Security Core Technologies (SCOR) v1.0 (Cisco Learning Library) – Cost:  $500
    Just like with the SISE exam, I’ve listed the retail cost here, but since I used Cisco learning credits this resource ended up being free to me.  I would still recommend it if you can afford it – or have learning credits available for use.  It makes a good companion to the printed materials and includes practice questions which aren’t carbon copies of those found in the OCG practice test.

    CCNP and CCIE Security Core SCOR 350-701 Complete Video Course (Pearson LiveLessons) – Cost: $129.89
    This video series is given by the same person who authored the OCG book, Omar Santos. I went into this with high expectations of exam-relevant content. If I had to do it again…I’m not sure I would invest in this product. About the only useful thing I got out of it were the practice test questions.

    Integrated Security Technologies and Solutions – Volume I: Cisco Security Solutions for Advanced Threat Protection with Next Generation Firewall, Intrusion Prevention, AMP, and Content Security (Cisco Press) – Cost: $56.28
    Integrated Security Technologies and Solutions – Volume II: Cisco Security Solutions for Network Access Control, Segmentation, Context Sharing, Secure Connectivity and Virtualization (Cisco Press) – Cost: $56.28
    After my second exam attempt, I think it was, these two books were recommended to me as resources by members of my study group. These are great resources. Again, you will not pass the exam with only these books, but I highly recommend them as a supplement to the OCG.

    Network Security Technologies and Solutions (Cisco Press) – Cost: $91.68
    I found this book on my own simply by browsing through the Cisco Press catalog of publications. It was not recommended to me, and I don’t believe anyone else in the study group used it. If you can afford to add this to your studies then I do recommend purchasing it. That said, if I had to choose only between this and the two volumes listed above, I’d pick those two.

    Exam Fees – Cost: $1,600.00
    Pretty self-explanatory here. Each exam attempt was $300, and I took it four times before I passed.

    In Retrospect…

    I spent a long time cursing the name of Omar Santos after this exam. I recently saw his name as one of the listed authors on a Cisco Press book that I was thinking about buying and immediately decided against it.

    In hindsight, I don’t know what kind of situation this exam was developed under…the material was the worst of any Cisco exam I have ever taken, but how closely did Cisco work to ensure that the material accurately reflected the exam?

    I don’t know, and I shouldn’t take that all out on Omar. I don’t even know the guy.

    My pockets are a lot lighter now and I’m fairly positive that I gained several new grey hairs (probably also lost a few permanently) as a result of this exam. But like I said before…I feel a great sense of accomplishment now that I have this certification, and I have gotten a fair amount of recognition from people I work with for having attained it.

    What’s Next?

    To be frank, I’m not really sure. I did take (and fail) the ENWLSD exam last year, mostly just because I thought it would be something quick and easy. I’m applying for some positions doing network security which require knowledge of Palo Alto firewalls and IPsec site-to-site VPNs, though, so I may pursue either the PCNSA or SVPN exams in order to bolster my knowledge with those solutions.

    I’m also roughly halfway through an associates degree program now which has severely limited my free time that I once used to study for certifications…but that’s not a terrible problem to have either.

  • Exam Review: Cisco SISE 300-715

    Back in late 2019, I made a decision that I was going to attempt to take the Cisco IINS 210-260 and SISAS 300-208 tests prior to the “Certpocalypse” of exams retiring in late February 2020.  My thinking was two-fold:

    1. My existing CCNA Cybersecurity Operations certification would be retitled as a “Cisco Certified CyberOps Associate.”  By passing the IINS exam I would be able to retain my CCNA status within the Security domain.

    2. The new exams being released after February 2020 would consist of a core exam and one or more specialty exams.  If I passed the SISAS test prior to its expiration, I would then only need to take one test – the SCOR – to convert that result into a CCNP level certification.

    Unfortunately, spoiler alert, I slacked off on my studies and did not make the progress that I had hoped I would.  I did eventually sit for the IINS exam but failed by a matter of just under 50 points.  Close, but no cigar.

    I sat idle for two or three months and brooded over my failure.  It had broken a streak of seven successful exam attempts in a row and I was miffed.  If only I had gotten three, maybe four more questions correct…

    Eventually I got over myself.  We had Cisco learning credits due to expire at work so I invested them heavily into the new exams.  I decided that I was going to make my goal of getting the CCNP Security certification come true, and I would do it prior to my year-end review – which is in October of this year.

    I selected the SISE 300-715 exam to begin with rather than the SCOR exam.  The SISE is one of several specialty exams for the new CCNP Security certification, and the updated version of the SISAS exam I was planning to take originally.  I chose this specialty specifically because I use Cisco ISE daily at work and I thought it would be a cake walk.

    What I learned, however, is that Cisco ISE has a lot more to offer than what we use it for, and I quickly began to feel like I was in over my head.

    Score Results

    First of all, I’ll admit that I’m not necessarily proud of the score or my individual topic results, but since the Cisco Press OCG book doesn’t release until October I’m not going to look a gift horse in the mouth on this one.

    There were several topics (like Web Auth and Guest Services) which were completely alien to me on a first pass over the material.

    My score breakdown by topic:

    • Architecture and Deployment – 67%
    • Policy Enforcement – 60%
    • WebAuth and Guest Services – 44%
    • Profiler – 86%
    • BYOD – 67%
    • Endpoint Compliance – 100%
    • Network Access Device Administration – 67%

    Study Materials and Cost

    For preparation, I used the following resources:

    CCNP Security SISAS 300-208 Official Cert Guide (Cisco Press) – Cost:  $105.23
    I messed up on this one by purchasing the book as a standalone item from Amazon back in 2019, which didn’t give me access to the practice test.  I ended up buying the e-book and practice test bundle separately in 2020.  If you absolutely, positively, have to take the SISE exam prior to October 2020, then this is for you.  Otherwise…wait for the revised edition to come out.

    CPLL-SISE-V3 Implementing and Configuring Cisco Identity Services Engine (Cisco Learning Library) – Cost:  $500
    I’ve listed the retail cost here, but since I used Cisco learning credits, this resource ended up being free to me.  I’d recommend it if you can afford it – or have learning credits available for use.  It makes a good companion to the printed materials and includes practice questions which aren’t carbon copies of those found in the OCG practice test.

    CCNP Security Cisco Identity Services Engine SISE 300-715 Complete Video Course (Pearson LiveLessons) – Cost:  $399.99  $129.89
    Cisco Press was running a discount on this video series for the new exams when I purchased it, so your mileage may vary.  I try to use as many different materials sources as I can, as having the same topic explained from multiple viewpoints can often help me assimilate that knowledge better myself.  For the cost I was happy with this course – although, since I only purchased it about 30 days before my exam, I did not end up making it all the way through the course.

    Network-Node.com – Cost:  Free
    Katherine McNamara is a Cisco engineer who holds multiple CCIEs and maintains a blog at network-node.com.  She has documented step-by-step Cisco ISE configuration steps for multiple ISE versions which helped explain technical material in a way that the Cisco Learning Library and Pearson LiveLessons videos just didn’t capture as well, and made perfect write-ups to follow along with if you’re labbing.

    LabMinutes.com – Cost:  Free
    This website contains a whole suite of free videos on multiple Cisco subjects, one of which is Cisco ISE – multiple versions of it at that.  There is an option to pay for downloads but you can very easily just stream the videos you’d like on demand from their website as well.  Unfortunately, this is another resource I only found out about only shortly before my exam was scheduled, so I didn’t get to use it for its full value.  If you’re just beginning your studies for the SISE exam definitely look this one up.

    Exam Fee – Cost:  $300
    I would be remiss if I didn’t include this cost.  Fairly standard as far as Cisco exams are considered.

    In Retrospect…

    I feel like the lack of a good practice test really didn’t help me much on this exam.  I did have the SISAS practice test from Cisco Press, but there are numerous differences between the SISAS and the SISE exams – namely, the SISAS is based on ISE v1.2 and SISE is based on ISE v2.4.

    There were also practice test questions included with the Cisco Learning Library Course, but I don’t feel like their difficulty was anywhere near what I encountered on the real exam.  The conceptual questions, sure, but not the specific configuration-based questions.

    Another opportunity for improvement on my part would have been labbing the principles I’m not familiar with.  I did download a trial version VM of ISE from Cisco but I had issues with the VM and had to reinstall it several times.  I never got as far as configuring profiles, guest access, or webauth portals as I intended to do, and ultimately ran out of time.  I feel like this lack of hands-on experience with configurations I have never performed is largely what contributed to my poor exam results.

    What’s Next?

    Now that I’ve passed the SISE exam – by the skin of my teeth – the only thing left to do is take on the SCOR exam.  In this case, luckily the SCOR book from Cisco Press is already available for purchase, so I shouldn’t have to try and reverse engineer the exam topics based on five year old material like I did with SISE.  There also seems like there’s a lot of carry-over in material from the IINS exam that I failed in February, which should hopefully make things easier for me before October.

    Here’s to hoping, anyway…

  • Cisco ISE 2.x: MAC Authentication Bypass (MAB)

    MAC Authentication Bypass (MAB) is a method of network access authorization used for endpoints that cannot or are not configured to use 802.1x authentication.  MAB uses the hardware address (MAC address) of the device connecting to the network to authenticate onto the network.

    This hardware-based authentication happens when a device connects to a Network Access Device (NAD) either wired or wirelessly – i.e., a switch, wireless access point, or VPN concentrator.  In this article I will be assuming that the NAD being used is a switch.

    Packets that are sent before MAB occurs and packets that are used to learn the MAC address are dropped by the switch.  Almost any packet can be used for MAB, but there are specific types of packets that cannot be used.  These include LLDP, spanning tree, and DTP packets.

    Once the switch learns the MAC address of the device attempting to connect to the network, the switch builds a RADIUS Access-Request packet using the MAC address of the device as the User Name and Calling-Station-ID.

    ISE then uses the MAC address from this RADIUS Access-Request packet to query its endpoint identity database for a match.  If a match is found, ISE returns an Access-Accept authorization to the switch and the device is allowed onto the network with a specific VLAN ID tag as configured by the ISE endpoint identity profile.

    If there is no matching endpoint identity in ISE, then the device is authentication session is put into an Unauth state and packets from that device are dropped by the NAD.

    Prerequisites

    In order for MAB to function, the switch must be configured to use the ISE server(s) for RADIUS authentications.  This configuration is outside of the scope of this article, and it is assumed that this configuration has already taken place.

    If issues are discovered with all MAB authentication on a specific switch, it may be best to troubleshoot the RADIUS configuration before troubleshooting MAB.

    MAB Host Mode Options

    There are four host mode options which can be used by MAB:

    Single-Host Mode:  MAB configured in single-host mode will allow only a single device to be allowed onto the network at a time.  If multiple devices are detected on the switchport, the switch will put the switchport into an err-disabled state.

    Multidomain Authentication Host Mode:  This host mode was created specifically for IP telephony.  Multidomain authentication allows one device to connect to each of the two switchport domains – one device can connect to the DATA domain, and one device can connect to the VOICE domain.

    Multi-Authentication Host Mode:  Multiple hosts are individually authenticated onto the network.  This host mode is used when there are multiple devices connecting to a single shared switchport through a hub or bridge such as an unmanaged switch.  Authorized devices are allowed onto the network as normal; packets from unauthorized devices are dropped and the switchport remains in the connected state.  This allows each device to be granted a specific VLAN ID according to its endpoint identity profile configured in ISE.

    Multihost Mode:  The first device to the network will be submitted to ISE for authentication.  If that device is authenticated, then the switchport will allow multiple other devices to access the network without requiring separate authentication of each device.  All connected devices will share the VLAN ID of the authenticated device.

    Typical Interface Configuration

    The standard interface configuration for deployments is as follows:

    mab
    authorization order dot1x mab
    authorization host-mode multi-auth
    authorization port-control auto

    Broken down, each of these commands accomplish the following:

    mab:  This command enables MAB on the interface.

    authorization order mab:  Establishes the order of authentication types to use.  Because MAB is typically used as a failover from 802.1x authentication, it is listed second.

    authorization host-mode multi-auth:  Specifies that MAB should use the multi-authentication host mode which allows multiple devices to authenticate onto the network each with its own VLAN ID.

    authentication port-control auto:  Turns on authentication for the switchport.

    Troubleshooting MAB

    Verify MAB status of an interface from the command line:

    show interface status | include [xyz]:  Confirm that the interface shows as connected.

    show interface status err-disabled:  If the interface shows err-disabled, this command will display the reason the interface is disabled.  This could be caused by issues such as single-host mode MAB with multiple devices connected or bpduguard.

    show run interface [xyz]:  View the interface configuration to ensure that the MAB commands are in place and complete.

    show mac address-table interface [xyz]:  Verify that the switchport has learned a MAC address for the device.  Note:  if the connected device has an Unauth session, you may not see a MAC address with this command.

    show authentication sessions interface [xyz]:  View the current authorization table for an interface.  This will display all MAC address learned by the interface as well as an Auth/Unauth status for each.

    show device tracking database interface [xyz]:  This command (specific to newer IOS versions) will display the MAC address and IP address of a connected device if device tracking is configured on the interface.  Some connection issues can be caused by a mismatch between a device with a static IP configured for a specific VLAN that does not match with the ISE endpoint identity profile.  This can also verify for VLANs with DHCP if the device has been unable to negotiate an IP address with its DHCP server by showing an APIPA address (i.e., 169.254.x.x).

    show ip device-tracking interface [xyz]:  Same command as above, but used for older IOS versions typically found on chassis-based switches.